Representative End User Clients







Representative Automation Clients







Representative Software Clients





Managing risk and adopting a risk-based approach to cybersecurity is increasingly necessary in the age of convergence. We’re already seeing a proliferation of risk-based services and approaches to cyber insurance, engineering, and design throughout the industrial and critical infrastructure segments. While many companies have their own methodologies for assessing risk, very few seem to focus specifically on manufacturing, infra-structure, or smart cities. So, how do we use risk assessments to craft cybersecurity policy for the operational technology (OT) domain?
The National Institute of Standards and Technology (NIST) has received considerable recognition over the past few years for developing the Cybersecurity Framework (CSF), which is now widely used as the basis for establishing effective security management systems. NIST recently released version 1.1 of its Framework for Improving Critical Infrastructure Cybersecurity. While this falls short of being a fully constructed risk management model for cybersecurity, the new framework does contain much expanded guidance on the element of risk in cybersecurity.
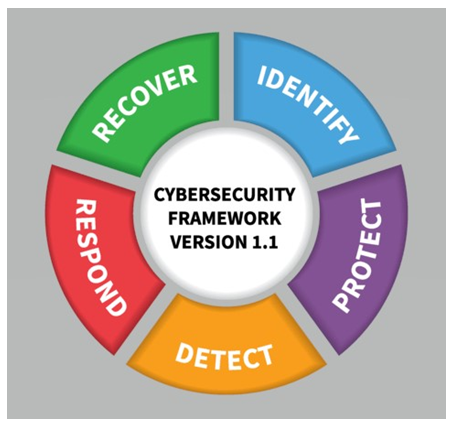 The US Commerce Department’s National Institute of Standards and Technology (NIST) recently released version 1.1 of its Framework for Improving Critical Infrastructure Cybersecurity, widely known as the Cybersecurity Framework. US Secretary of Commerce, Wilbur Ross, made an appeal to C-level management at all companies in the US to use the framework as the first line in their overall cyber-defense strategy.
ARC Advisory Group clients can view the complete report at ARC Main Client Portal or at ARC Office 365 Client Portal
If you would like to buy this report or obtain information about how to become a client, please Contact Us
Keywords: ICS Cybersecurity, NIST Framework, Risk Management, ARC Advisory Group.