Representative End User Clients







Representative Automation Clients







Representative Software Clients





Summary
Risk management is the foundation of effective industrial cyber security management. Since companies can't predict when or how a facility might be attacked they need to rely upon assessments of the risk of different threat scenarios to inform their cyber security investments in people, processes, and technology.
Unlike risk management for other industrial risk-based programs such as functional safety and project management, the dynamic nature of cyber risks makes cyber security risk management particularly challenging. New threats and vulnerabilities arise on a daily basis and can quickly undermine the effectiveness of established defenses. As a result, cyber security risk management requires ongoing risk assessments and maintenance of cyber defenses.
Maintaining cyber defenses is challenging for most industrial organizations. Cyber security expertise is limited and companies lack the information needed to focus resources on the most critical issues. Operating personnel often don't understand or realize their risk exposure and are reluctant to disrupt production schedules for security patches and software updates.
Executives from Honeywell Process Solutions recently briefed ARC Advisory Group on the company's new Industrial Cyber Security Risk Manager. The briefing demonstrated Honeywell's understanding of this critical situation and its commitment to helping industrial companies overcome these cyber security management challenges.
A Unique Approach to Managing Cyber Risks
Honeywell's Industrial Cyber Security Risk Manager addresses some of the biggest roadblocks to effective cyber security management. It is designed to help ensure that operators are always aware of their cyber risks and have the ability to direct cyber resources to areas that require immediate attention.

Honeywell Cyber Risk Manager Dashboard
Honeywell developed a unique approach to addressing these challenges. Industrial Cyber Security Risk Manager collects information in a similar manner as traditional security information and event management (SIEM) products, but converts this information into something that operators can understand and act upon. This includes notifications and alerts whenever security risk issues arise, plus an operator-friendly dashboard that helps operators understand the extent of these risks and the cyber security actions required. Drilldown capabilities help operators and cyber security personnel quickly isolate risks to specific devices and issues.
The software solution collects security information on an ongoing, non-disruptive basis from cyber devices throughout the plant. This provides information on endpoint security, network security, patch status, and backup status which is used to assess the risk posed by cyber attacks against the plant and devices within specific control zones. Endpoint security focuses on individual cyber devices. The associated risk assessments consider things like the status of anti-virus products and profiles, firewalls, admin privileges, etc. A similar approach is used for network security. This includes monitoring the status of individual network appliances (e.g., is it functioning and stable, errors, new MAC addresses, etc.) and what's happening in the network itself (e.g., communication errors, intrusion detection alerts, etc.).
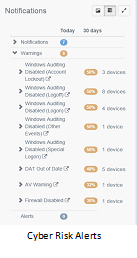
Every risk is assigned a numeric value that can be tuned for the specific environment. This is normally done during a mini-risk assessment of the site by the Honeywell services group. At the same time, the underlying security architecture (asset inventory, security zones, conduit models, etc.) is configured, enabling risk values to be grouped and propagated.
Risk appetite (the amount of risk an organization is willing to accept) and risk tolerance (the level at which action is required) are also tunable for each client. Risk appetite is used to define the yellow region on the dashboard, and tolerance the red regions. While initial values are established during the mini-site assessment, appetite and tolerance are challenging concepts and will likely require additional tuning during the initial rollout stage.
Honeywell also plans to introduce a compliance feature in future releases. Given Honeywell's strong position in the largely unregulated oil & gas industry, the initial focus will likely be on compliance with internal standards.
Recommendations
ARC research indicates that operator awareness and support for cyber security programs remains a major problem for industrial companies. Based upon our recent briefing with Honeywell, it appears that the Industrial Cyber Security Risk Manager addresses many of the underlying issues that are essential for every industrial organization to consider.
All signed-in ARC Advisory Group clients can view this report in pdf format at this Link
If you would like to buy this report or obtain information about how to become a client, please Request ARC Info
Keywords: Industrial Cyber Security, Risk Management.