Representative End User Clients







Representative Automation Clients







Representative Software Clients





In today’s hyperconnected supply chains, data is the currency of trust. It drives procurement decisions, inventory planning, shipping schedules, customs clearance, customer communications, and financial transactions. Yet as data flows across thousands of partners, its integrity and confidentiality are increasingly at risk.
When data is corrupted, manipulated, or exposed, the consequences ripple across entire ecosystems. A falsified shipment manifest can disrupt port operations. A leaked product design can erode competitive advantage. A manipulated sensor feed can halt factory production.
Executives must therefore focus not only on protecting systems but also on safeguarding the trustworthiness of the data itself.
Data integrity ensures that supply chain decisions remain accurate, reliable, and tamper-resistant.
Operational Impact: Corrupted demand forecasts can cause overproduction or shortages.
Regulatory Impact: Inaccurate customs filings can result in fines and shipment delays.
Financial Impact: Manipulated invoices can trigger fraudulent payments.
Reputational Impact: Leaked product designs or supplier contracts can erode trust.
For supply chains, integrity breaches are not abstract IT issues; they translate directly into physical disruption and financial loss.
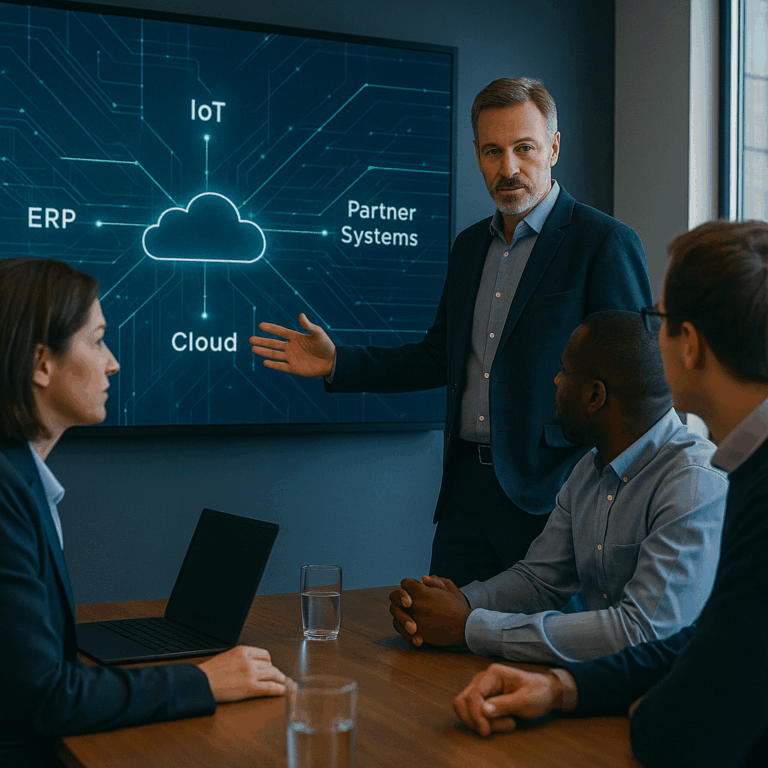
Modern supply chains exchange information through multiple digital channels:
ERP, WMS, and TMS systems.
EDI (Electronic Data Interchange) feeds.
Blockchain platforms.
Industrial IoT and OT sensor data.
Cloud collaboration tools.
Each exchange point introduces risk. Common attack vectors include:
Data Poisoning: Corrupting AI training data used in planning or optimization.
Man-in-the-Middle Attacks: Intercepting and altering documents in transit.
API Manipulation: Exploiting insecure integrations between partners.
Insider Leaks: Employees or contractors exposing confidential information.
The attack surface expands with every new supplier, integration, and cloud service.
Supply chains depend on collaboration, but collaboration requires sharing sensitive data, including designs, volumes, schedules, customer lists, and pricing. The challenge is enabling data sharing without compromising confidentiality.
Executives should evaluate:
Who has Access: Suppliers, subcontractors, freight forwarders, and authorities.
What is Shared: Only the minimum required data fields, not full datasets.
How it is Shared: Encrypted channels, tokenized identifiers, and anonymized records.
How it is Stored: Controlled environments with strict access logging and governance.
The guiding principle should be minimum necessary disclosure.
Several technologies help ensure that data remains authentic and unaltered:
Hashing: Digital fingerprints that detect tampering.
Digital Signatures: Validation of sender identity and message authenticity.
Immutable Logs: Write-once storage that prevents retroactive manipulation.
Blockchain and Distributed Ledger Technologies: Consensus mechanisms that prevent unilateral record changes.
Secure Time-Stamping: Verifiable chronology for transactions and records.
Executives should require end-to-end traceability of data provenance.
Encryption forms the foundation of confidentiality in shared supply chain environments.
At Rest: Encrypt databases containing sensitive designs, pricing, or contracts.
In Transit: Mandate TLS 1.3 or higher for all B2B data exchanges.
In Use: Confidential computing enclaves enable secure processing of sensitive data in memory.
Tokenization: Replace sensitive fields, such as customer identifiers, with non-sensitive placeholders.
A “no plaintext anywhere” approach is increasingly becoming a baseline expectation.
Executives should monitor advanced methods that enable secure collaboration:
Secure Multiparty Computation (MPC): Joint computation without revealing raw inputs.
Homomorphic Encryption: Computation performed directly on encrypted data.
Data Clean Rooms: Neutral environments where firms analyze shared data without exposing raw datasets.
Confidential AI: Models trained on encrypted or anonymized data to reduce leakage of sensitive information.
These approaches aim to balance data utility with privacy and confidentiality.
Intellectual property is among the most sensitive forms of supply chain data.
Design Leaks: Competitors may replicate products before launch.
Formula Theft: Particularly critical in pharma and food sectors.
Supplier Disclosures: Sharing CAD drawings or specifications increases exposure risk.
Executives should enforce:
Strong IP protection clauses in supplier contracts.
Access controls that restrict IP to authorized roles.
Digital watermarking to detect unauthorized redistribution.
Protecting IP is a strategic imperative.
A global pharmaceutical firm identified counterfeit drugs entering markets after attackers manipulated supplier invoices and production schedules.
Remediation steps included:
Adoption of blockchain-based serialization for each product unit.
Enforcement of digital signatures on supplier documentation.
Deployment of AI-driven anomaly detection to flag irregular orders.
The result was improved data integrity across the supply chain and reduced counterfeit risk.
Technology alone is insufficient. Data integrity and confidentiality require strong human and process governance.
Role-Based Access: Employees access only data relevant to their function.
Audit Trails: All data changes logged with user attribution.
Supplier Audits: Assessment of both cybersecurity and data handling practices.
Employee Training: Awareness of confidentiality risks, phishing, and insider threats.
Executives must ensure accountability across people, processes, and partners.
Why does this matter at the executive level?
Trust Equals Competitiveness: Firms with stronger data integrity gain preferential contracts.
Regulatory Compliance: Data protection regulations increasingly mandate confidentiality controls.
Risk Management: Integrity failures can escalate into operational crises.
Investor Assurance: Markets increasingly view data stewardship as a governance indicator.
For executives, data integrity is not routine IT housekeeping; it is a board-level trust issue.
Data integrity and confidentiality underpin trust in modern supply chains.
Attack vectors increasingly target APIs, EDI feeds, Industrial IoT sensors, and insider channels.
Integrity tools include hashing, digital signatures, immutable logs, and blockchain.
Confidentiality tools include encryption, tokenization, and confidential computing.
Emerging approaches include MPC, homomorphic encryption, data clean rooms, and confidential AI.
Intellectual property requires enhanced safeguards across supplier ecosystems.
Technology must be reinforced by human, contractual, and governance controls.
Executives should treat data stewardship as a strategic priority.
In Part 7: The Human Factor, the focus will shift from technology to people, examining how social engineering, insider threats, and organizational culture can influence cyber resilience even in well-architected systems.
Call to Action: Download the full guide to gain in-depth insights and practical frameworks that will help you lead the transformation towards a resilient supply chain.