Representative End User Clients







Representative Automation Clients







Representative Software Clients





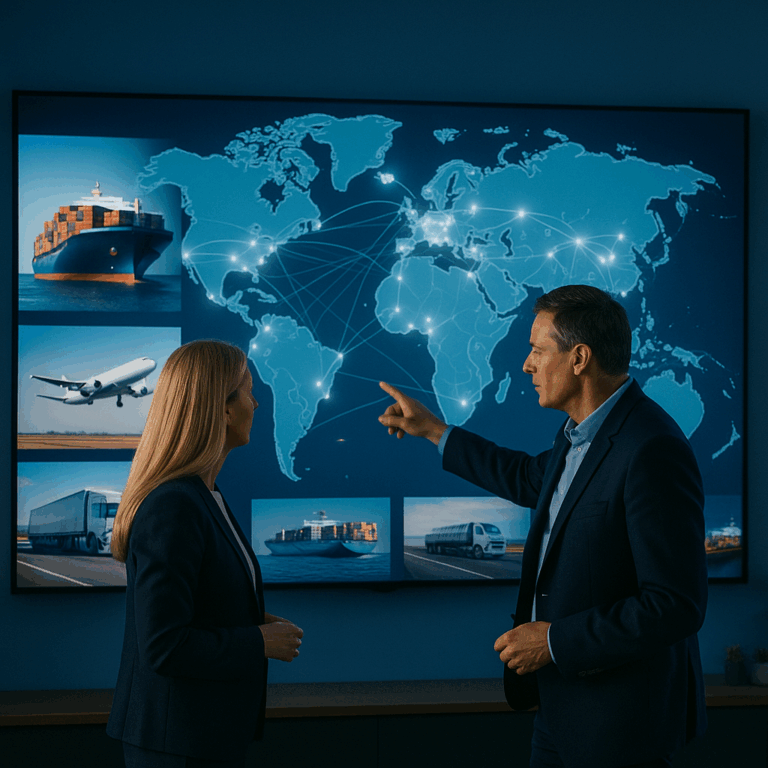
You cannot secure what you cannot see. That maxim defines the central challenge of modern supply chain cybersecurity. Today’s networks are so digitally entangled—across ERP systems, cloud services, IoT devices, and countless vendors—that many executives lack a clear line of sight into their true digital footprint.
Mapping the digital supply chain is therefore a prerequisite for resilience. It enables leaders to identify dependencies, understand data flows, and pinpoint where vulnerabilities may emerge. Without this visibility, organizations are effectively operating blind in an increasingly hostile environment.
Over the past decade, physical supply chains have been mirrored by complex digital ecosystems:
ERP (Enterprise Resource Planning): Core platforms for managing procurement, finance, and production.
WMS (Warehouse Management Systems): Orchestrating inventory, robotics, and fulfillment.
TMS (Transportation Management Systems): Optimizing routes, carriers, and fuel usage.
IoT Sensors: Tracking location, temperature, and condition of goods in real time.
Blockchain: Enabling distributed ledgers for provenance and authenticity.
AI and ML Systems: Forecasting demand, optimizing pricing, and predicting disruptions.
Each additional layer improves efficiency while expanding the attack surface.
Executives must move beyond system inventories to understand how data moves across the supply chain:
Procurement to Manufacturing: Supplier orders flow into ERP systems and feed production schedules.
Manufacturing to Logistics: OT data feeds WMS and TMS platforms.
Logistics to Customers: Tracking and delivery confirmations are shared through customer portals and APIs.
Cross-Border Operations: Customs clearance data passes through government systems.
Every handoff introduces a potential interception point.
A significant blind spot often lies beyond direct suppliers (third parties) and extends to suppliers’ suppliers (fourth parties):
Example: A logistics provider outsources cloud hosting to a SaaS vendor, which relies on a hyperscale data center. A breach at the fourth-party level can cascade downstream.
Challenge: Most organizations maintain visibility into direct vendors but lack insight into deeper tiers.
Response: Risk scorecards and contractual requirements that cascade security obligations down the chain.
Cloud adoption has reshaped supply chain IT, introducing agility alongside new dependencies:
Multi-Cloud Complexity: Organizations may use different cloud providers for ERP hosting, AI analytics, and IoT integration, each with distinct security profiles.
SaaS Ecosystems: Platforms integrate with dozens of applications through APIs, with misconfigured APIs now among the most common breach vectors.
Shared Tenancy: Sensitive workloads may coexist with those of other tenants, increasing exposure risk.
Mapping exercises frequently reveal unexpected vulnerabilities, including:
Legacy systems still operating in the background, often unsupported.
Shadow IT tools adopted outside formal IT oversight.
Supplier backdoors and remote access tools left open for convenience.
Overlapping credentials reused across multiple systems.
Executives are often surprised by the scale of unmonitored connections.
A structured approach can help organizations establish visibility:
Identify: Catalogue all digital assets, including ERP, SaaS, IoT, OT, APIs, and data lakes.
Classify: Prioritize assets by criticality, such as systems directly impacting revenue.
Map: Diagram data flows, access points, and interconnections.
Assess: Assign risk scores based on sensitivity, exposure, and vendor security posture.
Monitor: Continuously track changes such as new suppliers, applications, or system updates.
Technologies such as cyber digital twins can support real-time, continuously updated mapping.
A Fortune 100 retailer undertook a digital mapping exercise following a near-miss ransomware incident:
The review uncovered more than 400 shadow applications connected to core ERP systems, many via unsanctioned APIs.
Several suppliers’ IoT devices were found to be operating with default credentials.
The organization established a digital dependency map and introduced new contractual requirements for vendor cybersecurity standards.
The outcome was a measurable reduction in third-party exposure and increased confidence in operational resilience.
Blockchain and Distributed Ledgers: Improve provenance visibility but require careful security configuration.
Confidential Computing: Protects sensitive data while in use, reducing exposure during processing.
AI-Driven Discovery Tools: Automatically identify shadow IT, unmanaged endpoints, and rogue APIs.
These technologies enhance visibility but must themselves be securely deployed.
Mapping should be treated as an ongoing strategic capability rather than a one-time initiative:
Board Reporting: Cyber exposure maps can complement financial reporting.
M&A Due Diligence: Mapping digital dependencies of acquisition targets helps surface hidden risks.
Resilience Planning: Dependency maps enable simulation of cyber disruption scenarios and operational impact.
This reframes cybersecurity from a reactive IT concern into a core governance function.
Visibility is foundational to security.
Data flows are as critical as systems.
Third- and fourth-party risks represent major blind spots.
Cloud and SaaS interconnectivity amplifies exposure.
Blind spots persist across legacy systems, shadow IT, and supplier access.
Mapping is a sustained capability, not a discrete project.
In Part 4, Governance, Compliance, and Regulation, the focus shifts to how regulators, investors, and legal frameworks are shaping expectations for cyber resilience in supply chains.
Call to Action: Download the full guide for deeper analysis and practical frameworks supporting the development of a more resilient supply chain.