Representative End User Clients







Representative Automation Clients







Representative Software Clients





The SolarWinds presentation at the ARC 2021 Industry Forum shows why industrial companies need strategies to deal with the growing risks of software supply chain attacks. Industrial cybersecurity is a never-ending whack-a-mole game. Attackers find new ways to penetrate systems and defenders respond with new defensive measures. More sophisticated defenses drive more sophisticated, surreptitious attacks.
The SolarWinds attack demonstrates how far this game has progressed and how high the bar has been raised for an effective cybersecurity program. Software supply chain attacks exploit trust relationships with suppliers and extend the cyber battlefield beyond the province of individual companies. Defense against these kinds of attacks requires a collaborative effort among many different security teams.
Eric Byres, the CEO of aDolus and a well-known figure in OT cybersecurity, provided an informative presentation about the SolarWinds attack at the 2021 ARC Industry Forum. His talk demonstrated how a compromised update file affected 1,800 companies that use the popular SolarWinds Orion network management software. This resulted in persistent, unfettered access to confidential information of Fortune 500 companies, telcos, the defense and intelligence community, and even the White House. While there were no reports of OT systems being compromised, all defenders should take note.
SolarWinds was an extremely sophisticated attack, generally attributed to Russia. Regardless of who actually launched the attack, the resources required to execute it certainly suggests the involvement of a nation state.
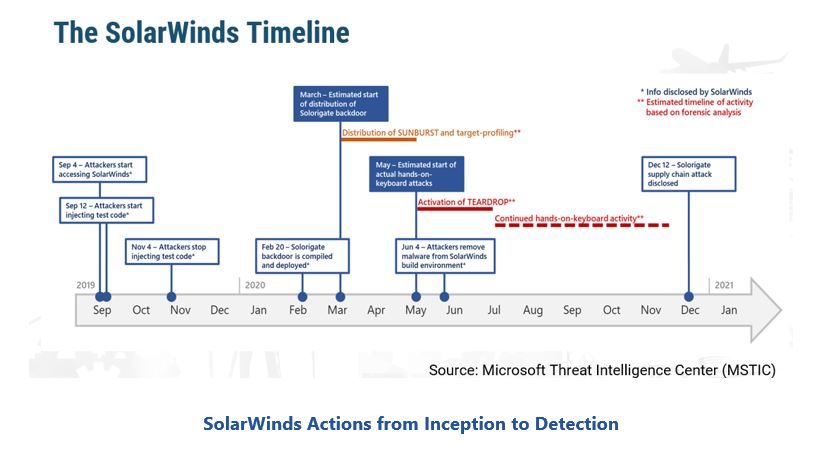
Most reports on this attack refer to a single malware package called Sunburst. But the actual attack involved a fifteen-month sequence of attacker actions, leveraging a collection of different malware and web shell components including Sunspot, Sunburst, Teardrop, Cobalt Strike, Beacon, and SuperNova that attackers used to progress their goals. These tools were so well designed that attackers were able to compromise some of the world’s most critical and well-protected IT systems.
Cyber criminals and nation-states strive to maximize the returns generated from their malicious cyber efforts. This fuels continuous development of more surreptitious ways to overcome defenses and more sophisticated malware to lengthen time before detection.
The SolarWinds attack demonstrates how supply chains amplify the effectiveness of both strategies. By exploiting supply chain trust relationships, an attack on one site gave the actors access to information in over 1,800 major companies and government agencies. While the effort to build and assemble the malware was extensive, this investment was repaid manifold with over seven months of unfettered access to droves of information and the opportunity to hide their tracks.
ARC Advisory Group clients can view the complete report at ARC Client Portal
If you would like to buy this report or obtain information about how to become a client, please Contact Us
Keywords: Software Supply Chain Cybersecurity, aDolus, ARC 2021 Industry Forum Americas, ARC Advisory Group.